
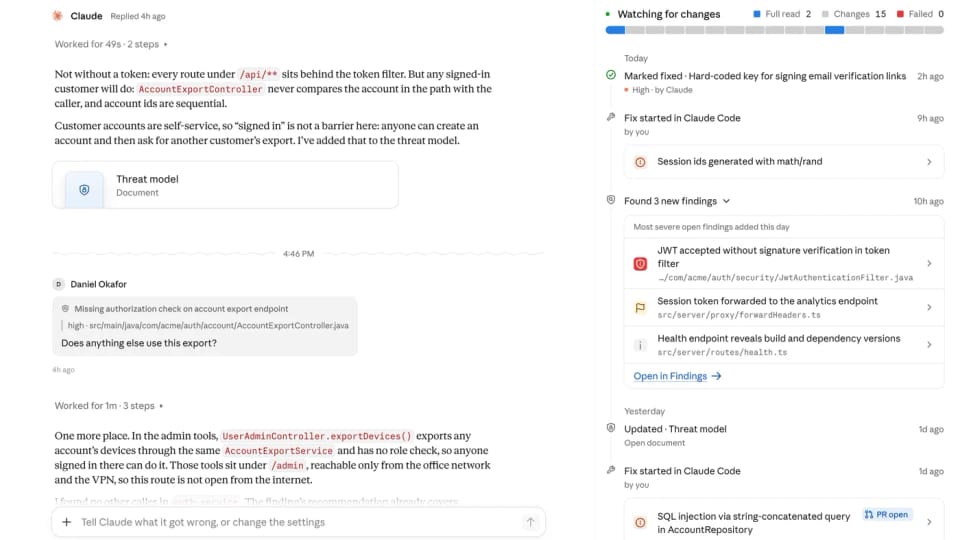
Anthropic has expanded Claude Security from individual repository scans into an ongoing vulnerability workflow. Its October 21 announcement describes continuous scanning, fix tracking and project context, available in public beta for Claude Enterprise customers. That availability matters: this is an enterprise beta, rather than a security feature automatically enabled for every Claude account.
From a baseline scan to recurring checks
According to Anthropic’s announcement, teams connect supported GitHub or GitLab repositories, choose their scope and start with a deeper baseline scan. Subsequent scanning follows code changes, with frequency informed by factors such as risk and complexity. Continuous scanning should therefore not be read as a promise that every commit receives an immediate, exhaustive review.
Projects can cover multiple repositories. That offers a way to investigate problems spanning services instead of treating each codebase as an isolated system. Teams still need to decide which repositories belong together and which branches matter for their deployment.
Findings can close and return
Claude Security tracks fixes when repaired code lands, including changes made outside Claude Code. If the issue appears again later, the finding reopens automatically. This turns the finding list into something closer to a maintained work queue than a one-time report.
Each project also has a knowledge base for deployment context and an editable threat model. Those inputs can help distinguish an externally reachable weakness from code used in a more constrained environment. Their usefulness depends on whether the team supplies accurate context and keeps it aligned with the system.
Connecting it to an existing workflow
The update includes APIs, webhooks and personal access tokens scoped to the issuing user’s permissions. Teams can bring findings into existing review and remediation processes without giving a token broader access than its owner.
A useful evaluation would compare the scanner’s findings with known issues, inspect proposed fixes and check whether resolved items stay resolved. Anthropic’s feature announcement establishes the workflow; it does not establish that a clean result proves an application secure.